New to CatchCPT? Get 5 free credits to spend on any lesson — automatically added when you register. Plus earn rewards when you refer friends. Get started
Understanding the Critical Need for Securing Artificial Intelligence Systems
2:00.3
Artificial intelligence is becoming a central technology in modern life, but its growing importance also makes it an increasingly attractive target for attackers. The title AI under attack captures a major shift in cyber security. The systems being protected are no longer only databases, networks, websites, and devices, but also models that learn, generate, classify, summarize, reason, and act. Traditional software can certainly be hacked, but AI introduces a different kind of vulnerability because its behavior is shaped by data, probabilities, prompts, and learned patterns rather than only by explicit code. An attacker may not need to break into a server or steal a password to cause harm. Instead, they may manipulate an input, poison training data, hide instructions in a document, trick an AI assistant into revealing sensitive information, or repeatedly query a model until they can imitate it. This topic matters because AI is being connected to email, financial systems, code repositories, medical tools, enterprise databases, customer service platforms, autonomous machines, and military decision support systems. As AI becomes more capable, the consequences of failure become more serious. A wrong classification, unsafe recommendation, leaked secret, insecure code suggestion, or unauthorized tool action can create real damage. This presentation explains why securing AI is harder than securing ordinary software, how adversarial inputs exploit model fragility, why prompt injection threatens language models and agents, how model theft and data leakage occur, and what defensive architectures can reduce risk. The main message is simple. Before society can safely depend on AI to protect important systems, AI itself must be protected from manipulation, misuse, and attack.
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
Unlock to access all lessons, quizzes, and a certificate.
Related courses
 Corporate FinanceSeptember 2026
Hong Kong Takeovers, Mergers and Share Buy-backs
Legal & Compliance
 Artificial IntelligenceSeptember 2026
AI, Copyright, and the Ownership of Training Data
Legal & Compliance
 Artificial IntelligenceSeptember 2026
From Chatbots to Agents: The Phase of AI
Legal & Compliance
 Digital AssetsSeptember 2026
Virtual Assets and Tokenised Securities: Regulatory Issues for Financial Intermediaries
Legal & Compliance
More from this course
Identifying Unique Cybersecurity Challenges Posed by Modern AI Models
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
1:56.7
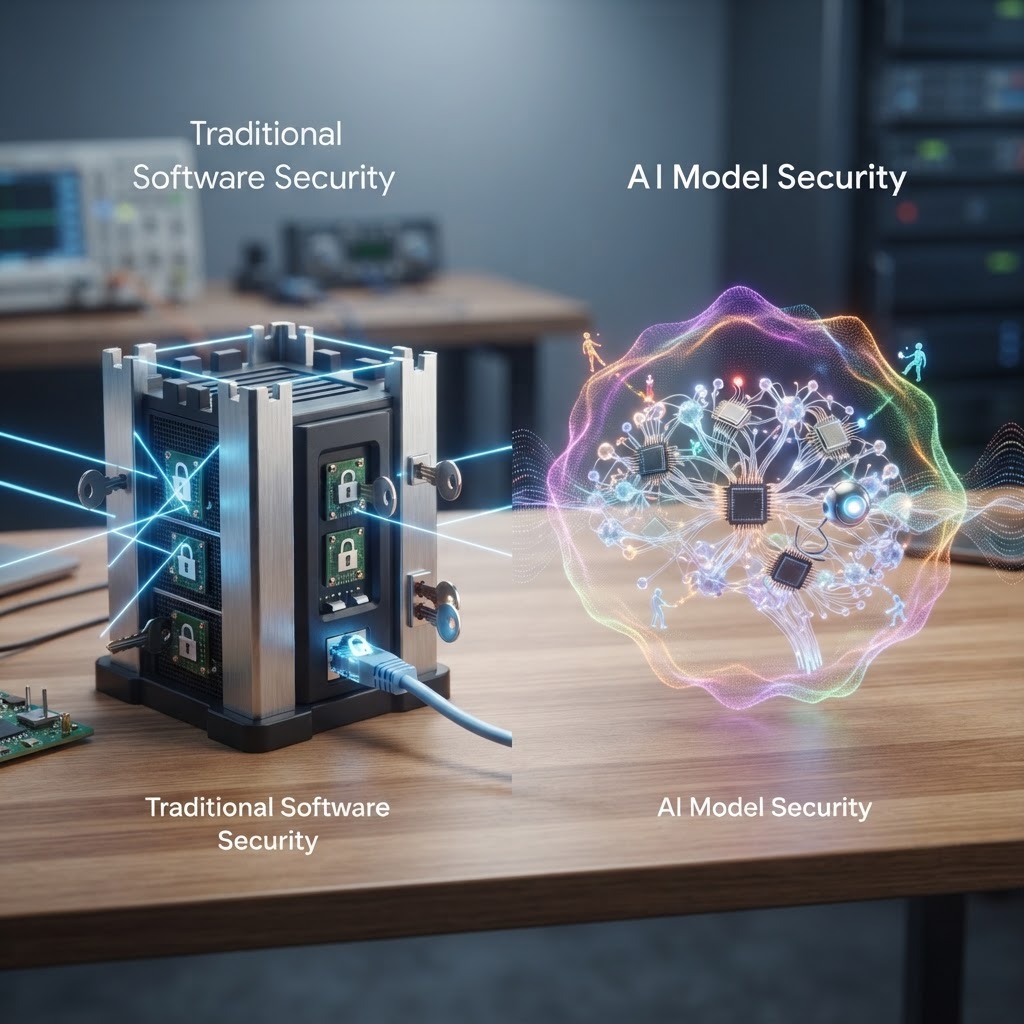
Differences Between Traditional Software Security and AI Model Security
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
1:59.5
Foundational Principles for Securing AI Systems and Data Infrastructure
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
1:59.8
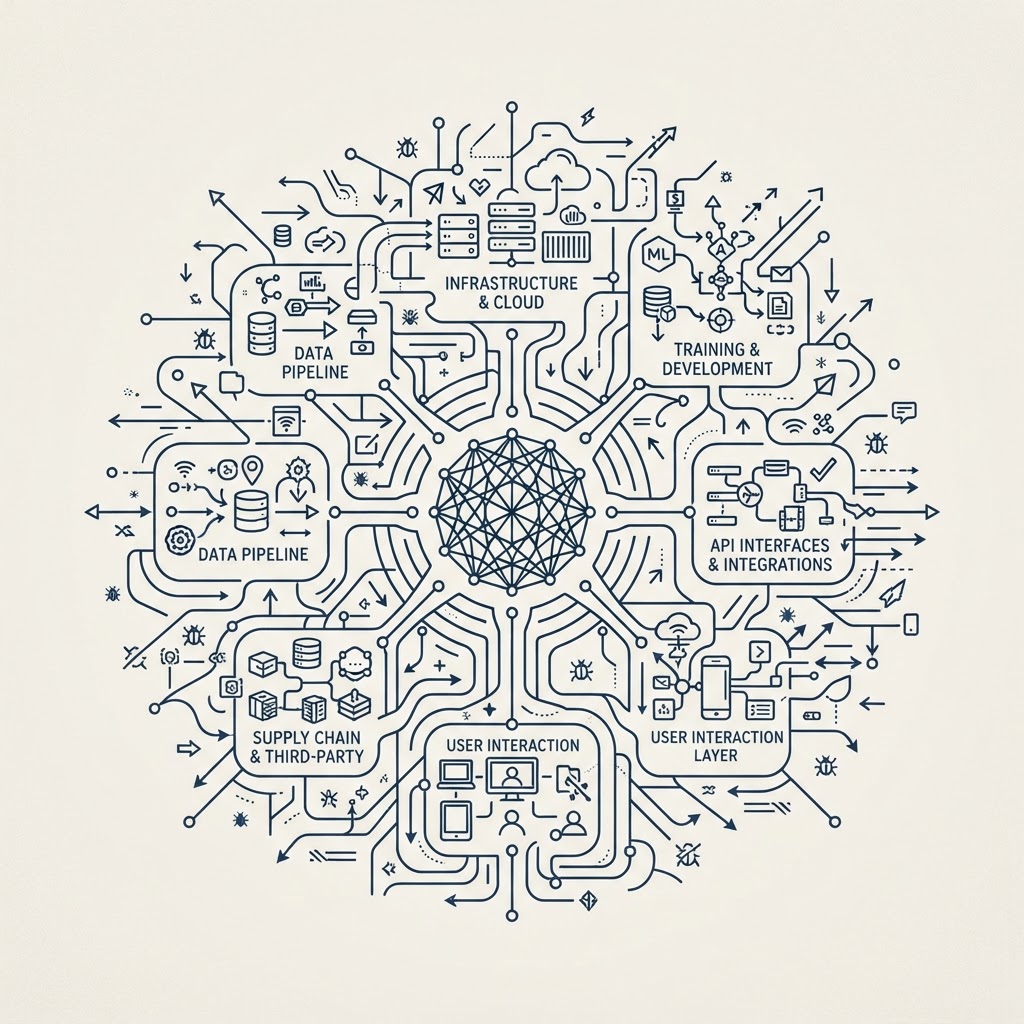
Mapping the Expanded Attack Surface of Modern AI Ecosystems
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
2:07.1
Related lessons
Hong Kong Takeovers and Share Buybacks Regulatory Framework
Hong Kong Takeovers, Mergers and Share Buy-backs
2:03.8
Ownership and Ethics of Training Data in Generative AI
AI, Copyright, and the Ownership of Training Data
1:55.4
Transitioning from Generative AI Chatbots to Autonomous AI Agents
From Chatbots to Agents: The Phase of AI
2:02.3
Regulatory Compliance Frameworks for Virtual Assets and Tokenized Securities
Virtual Assets and Tokenised Securities: Regulatory Issues for Financial Intermediaries
2:05.3