New to CatchCPT? Get 5 free credits to spend on any lesson — automatically added when you register. Plus earn rewards when you refer friends. Get started
Differences Between Traditional Software Security and AI Model Security
1:59.5
AI security is different because AI systems do not behave like ordinary deterministic software. Traditional software is usually written as a set of instructions. If a condition occurs, the program follows a defined path. When a bug appears, engineers can often trace the problem to a line of code, a failed dependency, or an incorrect configuration. AI models are different. Their behavior emerges from training on large data sets and adjusting millions, billions, or even trillions of internal parameters. These parameters do not operate like easily readable rules. They encode statistical relationships that allow the model to classify images, generate text, summarize documents, recommend actions, or write code. This creates a security challenge because the model may respond unpredictably to inputs that are unusual, ambiguous, adversarial, or outside its training distribution. Two prompts that look similar to a human may produce very different model behavior. A slight change in phrasing can bypass a safety rule. A hidden pattern in an image can alter classification. A misleading document can reshape the model's response during retrieval. Explainability is also difficult. Even when a model gives a confident answer, it may not be able to reliably explain why it produced that answer or which sources shaped it. Security teams must therefore defend not only software code, servers, and ARPIS, but also model behavior itself. That means testing for robustness, monitoring outputs, controlling access to sensitive data, validating tool use, and designing systems that assume the model may be wrong or manipulated. AI security expands cyber security from protecting execution paths to protecting learned behavior.
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
Unlock to access all lessons, quizzes, and a certificate.
Related courses
 Corporate FinanceSeptember 2026
Hong Kong Takeovers, Mergers and Share Buy-backs
Legal & Compliance
 Artificial IntelligenceSeptember 2026
AI, Copyright, and the Ownership of Training Data
Legal & Compliance
 Artificial IntelligenceSeptember 2026
From Chatbots to Agents: The Phase of AI
Legal & Compliance
 Digital AssetsSeptember 2026
Virtual Assets and Tokenised Securities: Regulatory Issues for Financial Intermediaries
Legal & Compliance
More from this course
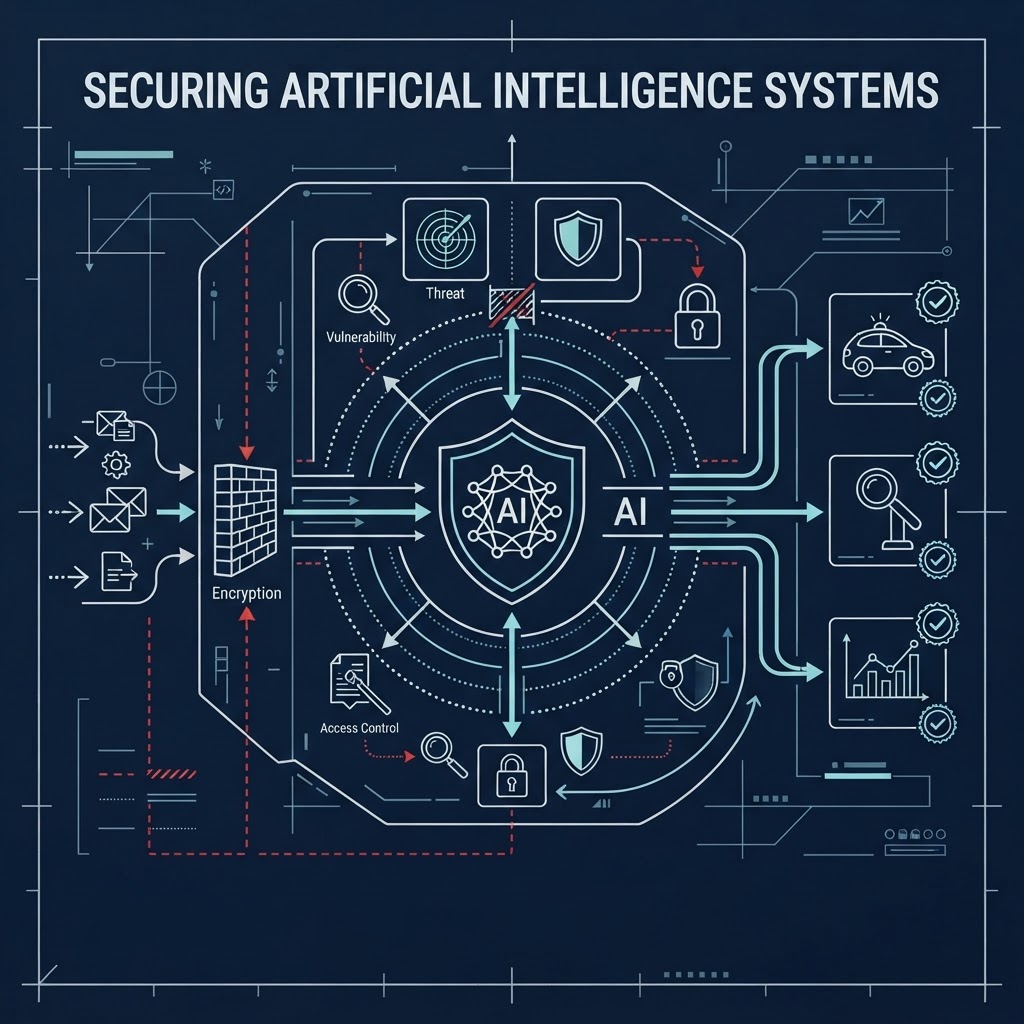
Understanding the Critical Need for Securing Artificial Intelligence Systems
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
2:00.3
Identifying Unique Cybersecurity Challenges Posed by Modern AI Models
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
1:56.7
Foundational Principles for Securing AI Systems and Data Infrastructure
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
1:59.8
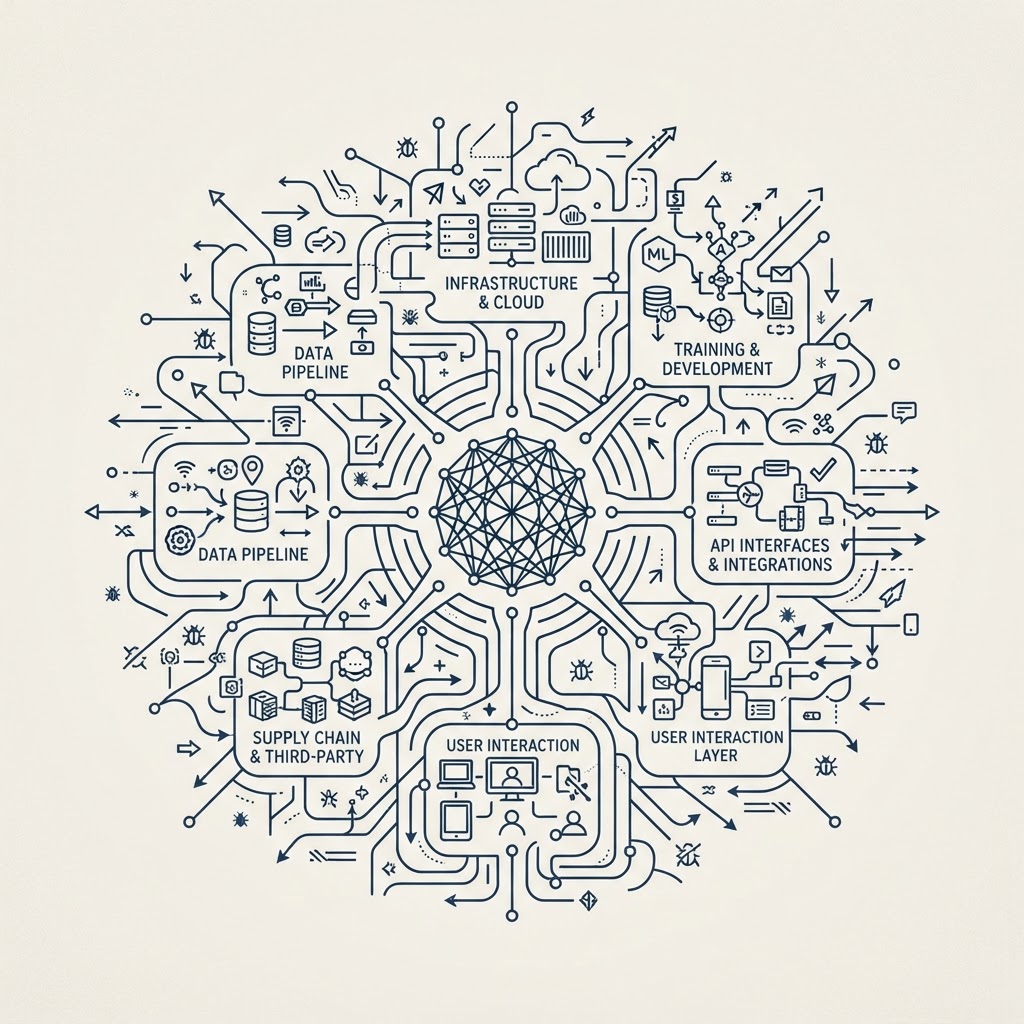
Mapping the Expanded Attack Surface of Modern AI Ecosystems
AI Under Attack: Adversarial Inputs, Prompt Injection, and Model Security
2:07.1
Related lessons
Hong Kong Takeovers and Share Buybacks Regulatory Framework
Hong Kong Takeovers, Mergers and Share Buy-backs
2:03.8
Ownership and Ethics of Training Data in Generative AI
AI, Copyright, and the Ownership of Training Data
1:55.4
Transitioning from Generative AI Chatbots to Autonomous AI Agents
From Chatbots to Agents: The Phase of AI
2:02.3
Regulatory Compliance Frameworks for Virtual Assets and Tokenized Securities
Virtual Assets and Tokenised Securities: Regulatory Issues for Financial Intermediaries
2:05.3